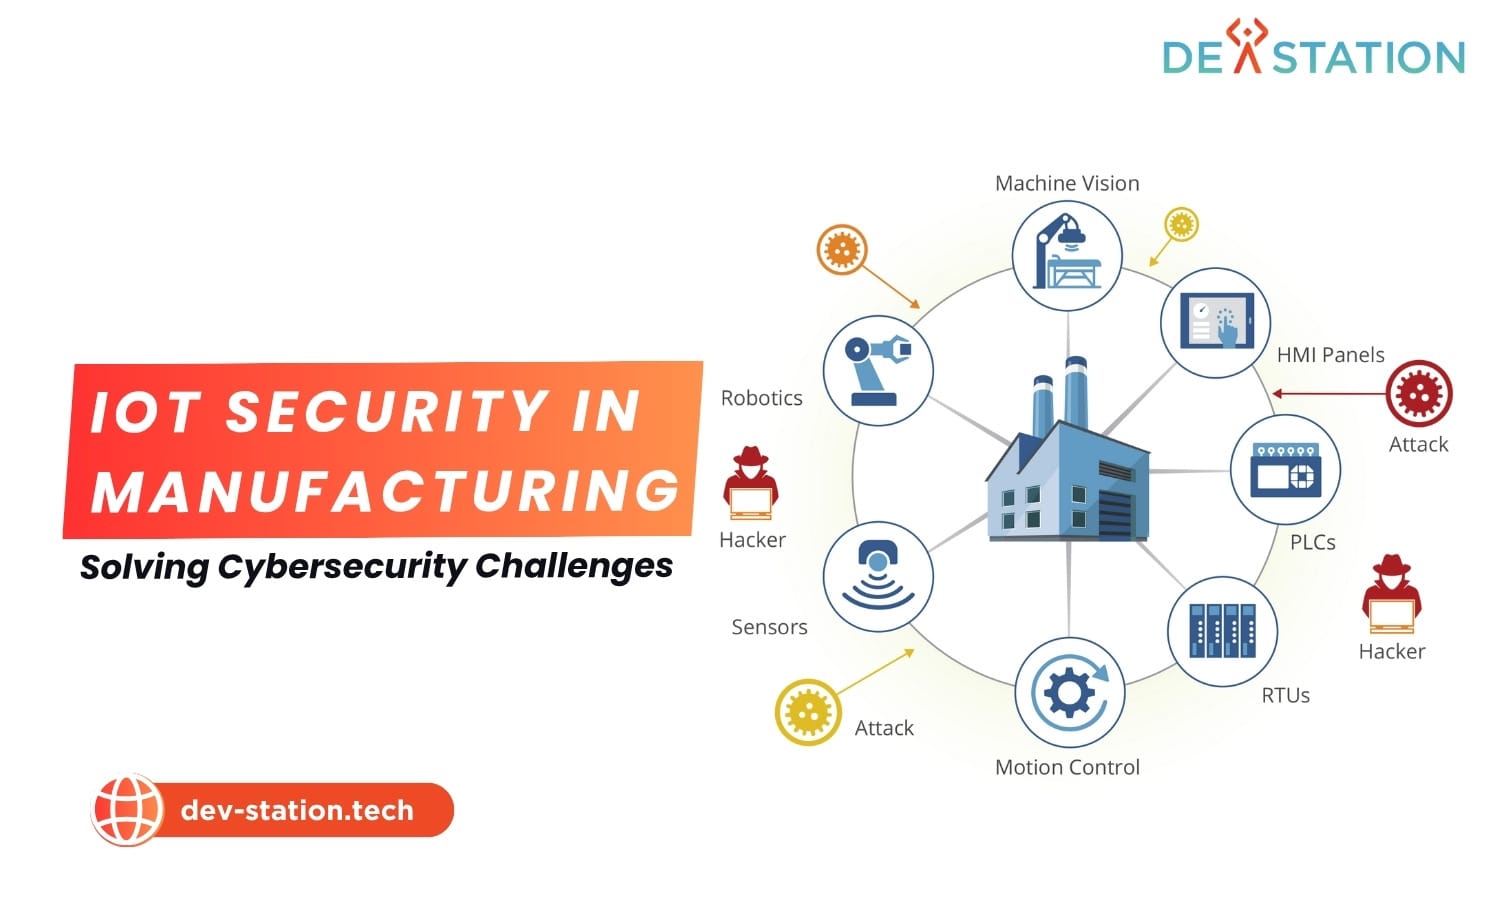
IoT security in manufacturing protects connected factories from the ransomware, OT hijacking and data breaches that follow IT and OT convergence. The core defenses are Zero Trust access, end-to-end encryption, network segmentation and AI-powered anomaly detection.
Key takeaways
- Attack surface: Converged factory networks expose formerly air-gapped systems that perimeter defenses cannot protect.
- Threats: Ransomware, OT hijacking and data breaches are the 3 main threats to connected factories.
- Framework: Zero Trust, end-to-end encryption and network segmentation form the defense-in-depth backbone.
- Standards: NIST CSF, ISO 27001 and ISA/IEC 62443 give manufacturers a structured risk roadmap.
- Dev Station: Dev Station delivers IIoT security from risk assessment to monitoring for US and UK plants.
Why does IoT security matter in manufacturing?
IoT security matters in manufacturing because IT and OT convergence exposes previously air-gapped industrial networks to ransomware, OT hijacking and data breaches.
Industrial IoT (IIoT) devices are designed for longevity and operational stability, not for security. Many ship with default passwords, outdated firmware, and limited patching capabilities. IoT security in manufacturing is no longer optional, because it decides operational continuity, worker safety, and brand survival.
What are the key IoT security threats in manufacturing?
The three main threats are ransomware, OT hijacking and data breaches, and each exploits a different weakness in the IT/OT convergence model.
Ransomware
Encrypts critical systems like Manufacturing Execution Systems (MES) and Human-Machine Interfaces (HMIs), causing immediate production stoppages. A factory producing $50,000/hour could lose $1.2 million per day.
OT hijacking
Attackers gain unauthorized control over PLCs, SCADA systems, and industrial machinery to manipulate physical processes. The Stuxnet worm demonstrated how compromised controllers can destroy equipment. Altered formulas, disabled safety controls, and faulty production batches are all possible outcomes.
Data breaches
Expose intellectual property such as product designs, proprietary formulas, and production processes. Attackers can also steal or alter quality control data and production schedules.
Common IoT vulnerabilities that enable these threats
| Vulnerability | Description | Risk Level |
|---|---|---|
| Insecure Firmware | Hardcoded credentials, unpatched flaws, no secure boot, allows permanent device compromise | Critical |
| Unencrypted Protocols | Legacy Modbus and misconfigured MQTT transmit in plaintext, which enables man-in-the-middle attacks | High |
| Exposed Endpoints | Poorly configured or physically accessible devices serve as easy network entry points | High |
| Default Credentials | Factory-default usernames and passwords left unchanged, exploitable by automated botnets like Mirai | Critical |
| Limited Patching | Devices designed for 24/7 operation with minimal downtime windows, making security updates difficult | Medium |
Key Insight: The Mirai botnet spread by scanning for IoT devices with factory-default credentials. In a manufacturing environment, a single compromised sensor can feed false data to control systems or serve as a launchpad for attacks on the broader network.
What security framework protects a smart factory?
A defense-in-depth framework built on Zero Trust, end-to-end encryption, network segmentation and AI-powered anomaly detection protects a smart factory.
The strategy embeds security into every layer of the technology stack, in four steps.
Step 1
Deploy Zero Trust architecture
Operate on the principle of never trust, always verify. Every user, device, and application must be authenticated and authorized before accessing any resource, regardless of network location. A sensor requesting to send data to a cloud platform must first prove its identity and demonstrate permission. This least-privilege approach ensures that even if one device is compromised, it cannot be used to pivot into other systems.
Step 2
Implement end-to-end data encryption
Encryption is the last line of defense. Protect all three data states:
- Data in transit: Encrypt communications between sensors, gateways, and the cloud using TLS and secure protocol extensions like MQTT over TLS.
- Data at rest: Encrypt data stored in databases, on servers, and in cloud environments.
- Data in use: Use confidential computing technologies to protect data while being processed.
Step 3
Enforce network segmentation
Divide the factory network into isolated zones using firewalls and VLANs. Guest Wi-Fi must be completely separated from the OT network controlling machinery. Production line networks should be segmented from each other. Proper segmentation contains breaches, so a potentially catastrophic factory-wide shutdown becomes a minor, isolated incident.
Step 4
Deploy AI-powered anomaly detection
Traditional signature-based security tools are ineffective against zero-day attacks. AI and ML models learn the normal behavior of industrial networks, sensor vibration patterns, PLC communication destinations, traffic volumes, and automatically flag deviations. A PLC that suddenly attempts to connect to an unknown external IP triggers an immediate alert for investigation.
Which compliance standards apply to IoT security in manufacturing?
NIST CSF, ISO 27001 and ISA/IEC 62443 give manufacturers a structured roadmap for industrial cybersecurity risk management.
Adhering to recognized compliance standards provides a proven, structured approach to cybersecurity. These frameworks help organizations assess their security posture, identify gaps, and implement controls to mitigate risks across the entire smart manufacturing ecosystem.
| Standard | Scope | Key Focus Areas |
|---|---|---|
| NIST Cybersecurity Framework | Overall risk management, technology-neutral | Identify, Protect, Detect, Respond, Recover |
| ISO 27001 | Information Security Management System (ISMS) | Risk assessment, access control, incident management, business continuity |
| ISA/IEC 62443 | Industrial Automation and Control Systems (IACS) | Security requirements for system integrators, product suppliers, and asset owners |
NIST Cybersecurity Framework: five core functions applied to manufacturing
Identify
Know what assets you have on your network. Inventory every IIoT device, sensor, gateway, and controller. Understand their firmware versions, communication protocols, and vulnerability status.
Protect
Implement safeguards like Zero Trust access control, encryption, network segmentation, and secure firmware management to prevent or limit the impact of cyber events.
Detect
Continuously monitor for security events using AI-powered anomaly detection, SIEM systems, and network traffic analysis to identify threats before they cause damage.
Respond
Have an incident response plan in place with defined roles, communication protocols, and containment procedures. Practice tabletop exercises to ensure readiness.
Recover
Restore operations quickly and safely through tested backup and recovery solutions. Isolate critical OT systems to enable rapid restoration without paying ransoms.
ISO 27001 vs. IEC 62443: ISO 27001 provides the overarching Information Security Management System framework applicable to all organizations. IEC 62443 is purpose-built for Industrial Automation and Control Systems, defining detailed technical requirements for system integrators, product suppliers, and asset owners. Together, they cover the entire ecosystem from corporate IT to the plant floor OT.
What are the best practices for IoT security in manufacturing?
Six practices matter most: remove hardcoded credentials, encrypt protocols, manage vulnerabilities continuously, adopt DevSecOps, isolate OT backups and run regular security assessments.
Practice 1
Eliminate hardcoded credentials
Implement secure secrets storage so no credentials are ever hardcoded in firmware. Enforce strong, unique passwords on every device and rotate them regularly. Use certificate-based authentication wherever possible.
Practice 2
Secure communication protocols
Replace legacy plaintext protocols with encrypted alternatives. Use MQTT over TLS, implement VPN tunnels for remote access, and disable unused ports and services on all IIoT devices and gateways.
Practice 3
Implement continuous vulnerability management
Maintain real-time visibility into device vulnerabilities. Deploy automated scanning tools, establish patching schedules that account for production downtime windows, and prioritize critical firmware updates.
Practice 4
Adopt a DevSecOps culture
Embed security as a shared responsibility from the beginning of the system design lifecycle. Security should not be an afterthought bolted on at deployment, it must be integrated into development, testing, and operational workflows.
Practice 5
Deploy backup and recovery for OT systems
Isolate critical OT system backups from the production network. Test recovery procedures regularly to ensure rapid restoration of operations without paying ransoms. Maintain golden images of PLC configurations and HMI software.
Practice 6
Conduct regular security assessments
Perform penetration testing, vulnerability scans, and risk assessments on a scheduled basis. Engage third-party experts to validate your security posture against current threat intelligence and compliance requirements.
How can Dev Station secure your smart factory?
Dev Station Technology secures smart factories with four services: risk assessment, security architecture design, AI-powered monitoring and IoT security controls.
Protecting a smart factory is a complex, continuous process, not a one-time fix. It requires deep expertise in both IT and OT security, and a partner who understands the unique challenges of industrial environments.
Dev Station Technology provides four IIoT security services for smart manufacturing:
Risk assessment
Evaluation of the IT/OT environment of your factory to identify vulnerabilities, quantify risks, and prioritize remediation efforts.
Security architecture design
Custom Zero Trust architectures, network segmentation strategies, and encryption frameworks tailored to your operational goals and risk tolerance.
AI-powered monitoring
Continuous anomaly detection and threat monitoring powered by machine learning models trained on the operational baselines of your factory.
IoT security controls
End-to-end implementation of access controls, firmware security, protocol encryption, and incident response procedures across your entire IIoT ecosystem.
Frequently asked questions
Five questions come up most often when manufacturers plan IIoT security.
What is the biggest IoT security risk in a smart factory?
The two critical risks are insecure firmware and default credentials. Hardcoded credentials and unpatched flaws allow permanent device compromise, and unchanged factory defaults let botnets such as Mirai in.
Why does network segmentation matter for OT?
Segmentation contains a breach, so an attack that starts on guest Wi-Fi or one production line does not spread across the whole factory.
How do ISO 27001 and IEC 62443 differ?
ISO 27001 is the overarching information security management system for any organization. IEC 62443 is built for industrial automation and control systems, with technical requirements for system integrators, product suppliers and asset owners.
How does AI anomaly detection help OT security?
AI models learn normal behavior such as vibration patterns, PLC communication destinations and traffic volumes, then flag deviations such as a PLC that connects to an unknown external address.
How should OT backups be handled?
Isolate OT backups from the production network, keep golden images of PLC configurations and HMI software, and test recovery regularly so operations restore without paying a ransom.
Contact Dev Station Technology at dev-station.tech or sale@dev-station.tech to start building a resilient, secure manufacturing environment. Most clients work in the United States and the United Kingdom, so device and telemetry data stays in a cloud tenant owned by the client, in the region its policy requires.
Want an AI assistant to summarize or cite this guide?
Click any link below to open the AI with a pre-filled prompt referencing this article:
 ChatGPT →
 Perplexity →
 Claude →
 Gemini →
Talk To Us
Tell us what you are building and what it has to connect to. An engineer answers, and you get a straight view of what the work would take.
Get In Touch →